On this page
Terabytes of credentials leaked in massive supply-chain attack centers on biz & it, supply chain attacks, and massive supply-chain attack, and Ars Technica is the primary source for the details below.
Key Points
- Biz & it, supply chain attacks, and massive supply-chain attack is the specific focus here, not the wider category around it.
- Any price, date, or spec not confirmed in the reporting is left unstated rather than guessed.
- Linked sources below cover this same subject, not just a related one.
Why This Matters
Terabytes of credentials leaked in massive supply-chain attack is a specific, source-reported update on biz & it, supply chain attacks, and massive supply-chain attack, not a general trend. It matters because it changes what is actually possible for people already working in this space, not just what sounds impressive.
Who this affects
This is most relevant to anyone already dealing with biz & it, supply chain attacks, and massive supply-chain attack directly, rather than as general background reading.
What Happened
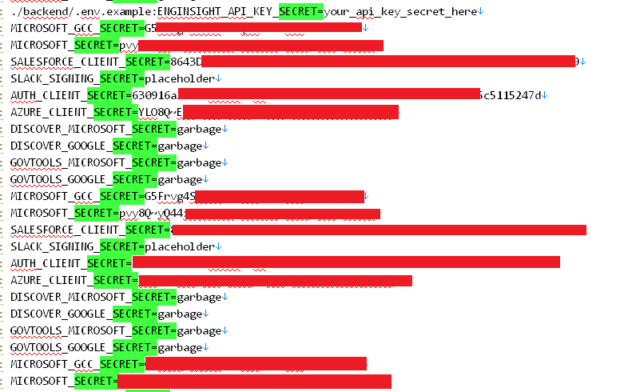
According to Ars Technica , Ars Technica reports on Terabytes of credentials leaked in massive supply-chain attack, covering biz & it, supply chain attacks, massive supply-chain attack, and 2 500 users. The LiteLLM compromise was the result of a previous supply-chain attack that infected the widely used vulnerability scanner Trivy.
Set aside the launch language and the practical question is simple: what changed, for whom, and starting when.
Key Details Readers Should Know
Credit: Hudson Rock Credit: Hudson Rock A full list of organizations is here . Anything not stated directly, such as an exact price, date, or specification, is treated as an open question rather than a fact.
A specific detail worth noting
London Stock Exchange Group (LSEG) Thomson Reuters FedEx Munich Remunichre.com MediaTek Inc.
Practical Impact
For everyday users, the impact depends on whether this removes a real step from a workflow or just adds another option to evaluate.
Early access and general availability behave very differently in practice, so treat a preview as a preview.
Editor’s note: This article keeps claims narrow and grounded in the reporting above so readers can compare, wait, or act with confidence.
A Practical Checklist Before You Adopt It
Check what it actually replaces in your current workflow, whether it works with your existing tools, and what happens if you need to switch back. Note anything still marked as limited, beta, or invite-only, since that changes how much to rely on it right now.
What to Do Next
The next step depends on how biz & it, supply chain attacks, and massive supply-chain attack connects to something you are already doing or plan to do.
For casual readers
Hold off on changing your current setup until more real-world usage reports come in.
For power users
Test it against your current tool on the same task and compare setup time, output quality, and cost side by side.
Ayxworks Takeaway
Terabytes of credentials leaked in massive supply-chain attack comes down to specific facts from Ars Technica, not a general trend claim. The signal is real, but the right move is to match it against your own workflow before treating it as a must-have.
Biz & it, supply chain attacks, and massive supply-chain attack is the concrete detail to remember here, not the headline framing.
Want more practical guides? Explore more Ayxworks insights and save this article for later.
Hudson Rock instructed any organization that uses any AI proxy infrastructure, third-party CI/CD vulnerability scanners, or downstream AI packages to immediately audit their environment for versions 1.82.7 and 1.82.8 of LiteLLM, the two compromised versions of the software.
The firm advised all those affected to perform “aggressive credential revocation,” assume any secret accessible to the LiteLLM environment is compromised, invalidate and rotate all cloud keys, Kubernetes service account tokens, and GitLab/GitHub PATs, and audit logging and egress filtering.
FAQ
What is the main point of Terabytes of credentials leaked in massive supply-chain attack?
Ars Technica reports specifically on biz & it, supply chain attacks, and massive supply-chain attack; that is the core fact this article covers.
Why does biz & it, supply chain attacks, and massive supply-chain attack matter?
It matters when it touches a decision, routine, or budget you already have; otherwise it is useful background rather than an action item.
Does this article add claims beyond the source?
No, this article does not add claims beyond Ars Technica’s reporting; anything not stated directly is left as an open question instead of a guess.
What should I do with this information?
Check the specifics of biz & it, supply chain attacks, and massive supply-chain attack against your own situation before treating it as settled.
How were supporting links chosen?
Only links that discuss the same specific subject were kept; loosely related coverage was left out so the citations stay relevant.
External Sources and Further Reading
- Ars Technica: Terabytes of credentials leaked in massive supply-chain attack
- Ars Technica: Researchers found a way to hijack devices through Zoom screen sharing
- MIT Technology Review: Scaling AI agents with trustworthy data
- Ars Technica: Twitch content has trained Amazon AI for years, but users can opt out now
- The Verge: Twitch streamers can now opt out from training Amazon’s AI